Justin Drake Urges Bunker Mode Over AI Encryption Risk

This article has been reviewed and verified for accuracy by our editorial team. All claims, data points and platform details are cross-referenced against primary sources.
- Data accuracy verified
- Sources cross-referenced
- Platform details confirmed
Some links on this page are affiliate links. Datawallet may earn a commission when you sign up through them, at no extra cost to you. This never influences our editorial ratings, rankings or recommendations.
Read our full disclosure
GM. Ethereum Foundation researcher Justin Drake urged the industry to start planning for bunker mode, moving funds to fresh addresses before elliptic-curve cryptography potentially breaks ahead of q-day.
Elsewhere, Vitalik Buterin warned against hasty wallet migrations, the US government shifted $1 billion in seized bitcoin, and ESMA gave EU platforms three months to drop non-MiCA stablecoins.
Everything you need from the past 24 hours sits below. 👇
01
Justin Drake Urges Bunker Mode Over AI Encryption Risk
Justin Drake, a researcher at the Ethereum Foundation, called for bunker mode planning, urging holders to shift most assets into fresh addresses whose public keys stay hidden behind a hash. He stressed this is a personal recommendation, and that nothing in existing cryptography has broken.
His worry is that the Elliptic Curve Digital Signature Algorithm, which secures Bitcoin and Ethereum transactions, cracks before q-day, when quantum computers overpower public-key cryptography. Drake framed a break as recovering a key inside one week on a GPU cluster, with the worst case landing in months rather than years.
Drake named Binance, Bitbank, Robinhood, Bitfinex and Tether as firms that should harden cold storage, citing Project Eleven's Bitcoin Risq List of 14 million addresses with exposed public keys. Wallets under 50 BTC enjoy what he called Satoshi's shield, since roughly 20,000 exposed Satoshi addresses each hold 50 BTC.
Drake pinned the urgency on OpenAI's release of 722 mathematical manuscripts from an internal model, evidence in his reading that mathematical superintelligence is upon us. He favors hash-based security over systems with heavy mathematical structure, and says exiting bunker mode would demand what he calls post-AI cryptography.
Today I call upon the blockchain industry to calmly begin planning for "bunker mode". My personal recommendation is to set in motion a controlled mass migration of assets to fresh addresses, i.e. addresses whose pubkeys remain hidden behind a hash. Holders, starting with large and sophisticated ones, should consider moving the bulk of their funds to addresses that have never signed a transaction. And when they do sign one, they should also move remaining funds to a new address (possibly generated from the same seed phrase). Don't rush. While I believe there is cause for action a rushed migration would do more harm than good. Don't panic either. Moving assets to protected addresses is a simple, preventative step which does not require new cryptography or new wallets. IMO it is now reasonable to brace for the possibility that ECDSA breaks before qday, in the worst case in months not years. By "break" I mean fast private key recovery (e.g. in one week) on available hardware (e.g. a large GPU cluster). Recent days have been humbling for human mathematical intuition. Long-held, unquestioned hypotheses have fallen. This includes the n log(n) bound for integer multiplication and the 3SUM conjecture. In hindsight, May's unexpected disproof of the Erdős unit distance conjecture was our warning shot. Yesterday's OpenAI drop made it clear that mathematical superintelligence is upon us. They say there are weeks where decades happen. We are about to live through weeks where centuries of mathematical progress happen. Could our magic 64-byte ECDSA signatures be too good to be true? Was it just security through obscurity all this time? Elliptic curves feel especially vulnerable to superintelligence. Curves carry rich structure, with room for fancy tricks like Schoof, Frobenius, pairings. (By contrast, hashes are designed to minimise algebraic structure.) Separately, as Ewin Tang can attest, an efficient quantum algorithm sometimes foreshadows an efficient classical one. We should be open to the possibility of a classical counterpart to Shor that breaks elliptic curves and RSA at once. Also noteworthy is the striking under-representation of cryptographic breakthroughs among the 722 mathematical results OpenAI published. I've witnessed first-hand the US government censoring academic quantum cryptanalysis results. Backroom interventionism is my base case. I urge large, sophisticated actors to lead by example. Project11's "risq list" (bitcoin-risq-list.projecteleven[.]com) is a great tracker of exposed BTC pubkeys. Binance, Bitbank, Robinhood, Bitfinex, and Tether have an opportunity to harden their cold storage. Next month I'll address institutions in London in a live Q&A (forum.ethereuminstitutional[.]org/london-2026). Again, please do not rush. Wallets holding under 50 BTC enjoy partial cover from "Satoshi's shield", i.e. his 20K exposed addresses that hold 50 BTC each. Load-bearing signers like oracles and L2 security councils should consider rotating ECDSA pubkeys with every signed message and/or multi-signing with a hash-based schemes like SPHINCS. Exiting bunker mode safely will require post-AI cryptography. My inclination is to go all-in on hash-based cryptography and avoid structured mathematical assumptions entirely, whether from curves, lattices, or isogenies. A single battle-tested hash (e.g. from the SHA or BLAKE families) yields plausible post-AI security. The Ethereum roadmap on strawmap[.]org fully embraces hash-based cryptography with end-to-end formal verification as a response to the quantum threat. Those timelines must now be revisited and accelerated in light of mathematical superintelligence. I'll be pushing for maximum defensive acceleration.
— Justin Drake (@drakefjustin) October 7, 2026
02
Buterin Warns Against Hasty Wallet Migrations
Ethereum co-founder Vitalik Buterin cautioned against scrambling to migrate funds, writing on X that botched upgrades have cost him more than hacks ever did. Keeping coins in a fresh crypto wallet that has never signed a transaction is a sound precaution, he said, provided the move is easy to execute.
AI-accelerated mathematics is why ECDSA could fall early, Buterin argued, predicting lattice concrete security takes serious hits from the next two years of AI math. He flagged ML-DSA, fully homomorphic encryption and lattice schemes as the core risk, urging privacy protocols to keep encrypted notes offchain.
I don't recommend anyone scramble to move their funds to new wallets today. But we should take the risks to cryptography from AI-accelerated math seriously, and minimize our exposure to not just quantum-vulnerable cryptography, but also potentially AI-vulnerable cryptography. The core new area of risk from this viewpoint is, unfortunately, ML-DSA / FHE / lattices. (and it's also another reason, along with quantum, why ECDSA might fall even faster than expected, hence the "fresh address" recommendation) So far most people have been in the mode of thinking "elliptic curves broken, hashes safe, lattices safe". But there is a good chance that the concrete security of lattices will take serious hits from the next two years of AI math. The basic threat model is: factoring is something that naively takes 2^(n/2) time, but over decades smart people have found and optimized number field sieves, and degraded that to 2^O(n^(1/3)), which is why RSA keys and signatures need to be ~400 bytes (and not 64 bytes). What if there are skeletons in the closet like that, both for elliptic curves and lattices, that we are simply not smart enough to discover - but bots soon will be? This is a major part of the reason why for the past year ethereum's lean roadmap has been going in the "hash-only" direction: no lattices, no ML-DSA, no Falcon, no lattice-based commitments inside ZK proofs, etc. Signatures in lean ethereum are all hash-based, either WOTS or SPHINCS-. For signatures and proofs, we already know how to go hash-only. The bigger challenge is for *public-key encryption* - and this goes far beyond blockchains. Secure communication, anonymizing protocols, lots of things need public-key encryption. And unfortunately there are long-standing mathematical theorems showing why public-key encryption cannot be done with hashes alone. You have to have some kind of trapdoor object that has at least one form of usable "structure" - either group theory (incl. isogenies) or lattices or code-based or potentially in the future even more newfangled and spooky things (local mixing?). But for anything that has structure, you should assume that AI will make at least some progress in breaking that structure. Here, one reasonable inference is that if you want to make something plausibly long-term secure, multiply the key sizes by 10. To me that's a very plausible world and something not at all extreme to predict. If AI will bring us 50 years of math in 2 years, then that 50 years of math may very plausibly include a "naive factoring -> GNFS" level of improvement to our ability to break lattices. In that world, lattices will still exist, but they will have to be significantly bigger to guarantee the same level of safety. And at those new larger sizes, hash-based constructions will beat lattice-based constructions on concrete efficiency in every use case where hash-based constructions are possible at all. Theoretically, of course it's possible that hashes are broken too (eg. P = NP would imply that). But I think P = NP is very unlikely. And intuitively, it's much more likely that a mathematical object has exactly no exploitable structure (like hashes are intended to), than that a mathematical object has exactly ~3 forms of exploitable structure (for elliptic curves: associativity, Schoof, pairings) and not some secret fourth form of structure we have not yet discovered that greatly degrades its security (for elliptic curves, ECDLP and pairing security). Similar for LWE, SVP, RLWE and the zoo of lattice problems. For this reason, we do not yet see any reason to worry and start padding the byte size of hashes (if we start to worry more, we would pad the round count first before doing anything to the byte size). Concrete TLDR, my own personal views: * Hash-based > lattice-based, in those situations where hash-based is possible at all * For anything lattice-based, be much more paranoid on param sizes. Remember that blockchains are only a small portion of the cryptography story; this point goes far beyond blockchains and applies to eg. access to websites, secure messaging, Tor / VPNs ... * For privacy protocols, strongly favor NOT putting encrypted notes onchain. Instead, send them offchain through some third-party mechanism. * If it's not difficult for you, keeping your funds in addresses which have not yet been used to make a transaction is a good idea. If it's easy for you, do it. **But be careful about migrations; I personally have lost more money in botched migrations than I have lost in all hacks combined**. * For multisig wallets, doing confirmations offchain is better than onchain, because this way the signatures of signer wallets do not get exposed to the public, so if ECDSA falls to AI much faster than expected, at least the multisig "gracefully degrades" to a 1-of-1 where the 1 is whoever was gathering the signatures - a much better place to be than "anyone can take the money" https://t.co/oVjwZog2lL
— vitalik.eth (@VitalikButerin) October 7, 2026
03
US Government Shifts $1 Billion Bitfinex Hack Bitcoin
A wallet Arkham labels as holding the Bitfinex hacker's seized coins moved 12,267 BTC, worth about $1.01 billion, to a fresh unlabeled address at 9:33 a.m. ET. Nearly all of it landed there, with 0.0012 BTC routed to a second wallet, and Arkham marks both outputs as already spent.
The haul belongs to roughly 94,000 BTC seized in 2022 from Ilya Lichtenstein and his wife Heather Morgan, and follows Wednesday flows of $119 million in USDT to Coinbase Prime. Washington still holds about 306,795 BTC, near $24.85 billion, earmarked for a bitcoin reserve that will not be sold.
LATEST: U.S. government-linked wallets moved 12,267 BTC ($1.01 billion) from a Bitfinex hack seizure wallet to new, unlabeled addresses. No exchange deposit was recorded, which points to wallet reshuffling rather than a sale. https://t.co/21hgXAO5HQ
— CoinDesk (@CoinDesk) October 8, 2026
04
ESMA Gives EU Platforms Three Months to Drop USDT
The European Securities and Markets Authority ordered authorized platforms to stop letting EU customers buy, trade or swap stablecoins that fall outside MiCA, setting a deadline of January 8, 2027. The opinion names no tokens, though Tether's USDT is the standout unauthorized example, alongside PayPal's PYUSD.
During the wind-down, venues may only help users sell, convert, withdraw, transfer or safekeep the tokens, never purchase, promote or trade them. National regulators decide how each platform resolves client balances, and ESMA argues leaving the coins available would erode the reserve and redemption rules binding MiCA-licensed exchanges.
🇪🇺 REGULATION: ESMA gives EU crypto firms face a Jan. 8 deadline to unwind exposure to non-MiCA-compliant stablecoins. https://t.co/29VBDKcMS2
— Cointelegraph (@Cointelegraph) October 8, 2026
05
Data of the Day
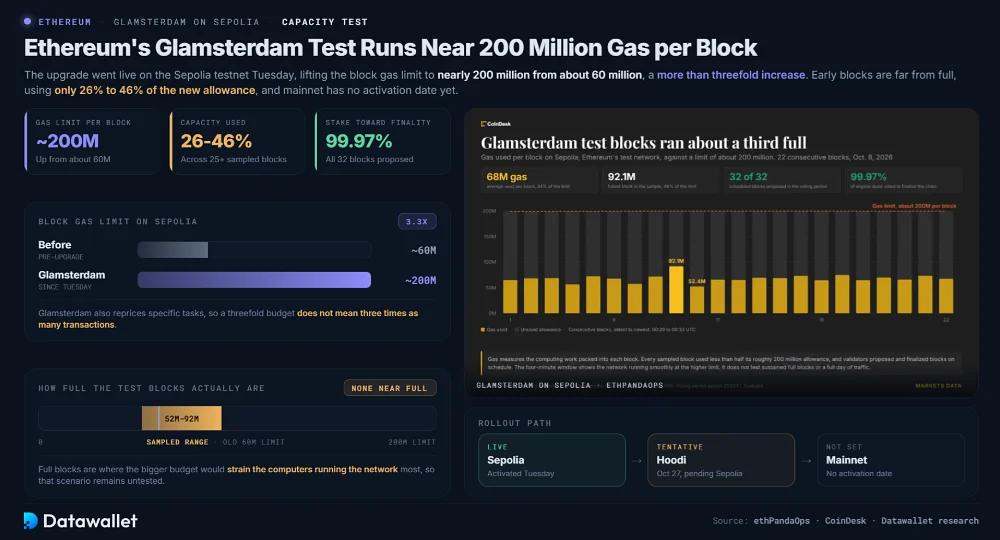
Ethereum's Glamsterdam upgrade went live on the Sepolia test network, lifting the per-block processing budget to nearly 200 million gas from roughly 60 million. Sampled blocks used only 26% to 46% of that allowance, or about 52 million to 92 million gas each, none running close to full.
A six-minute voting window produced all 32 scheduled blocks, with 99.97% of eligible testnet stake voting toward finality. The Glamsterdam upgrade also reprices data creation and access, so developers must retest apps assuming fixed gas costs, with Hoodi tentatively slated for October 27 and mainnet still undated.
06
More Breaking News
- Securitize launched 12 tokenized US stocks on Solana, including Apple and Nvidia, with Jump Trading supplying liquidity ahead of planned tokenized stock exchanges at NYSE and OKXICE.
- Samsung Wallet will carry USDC on Solana for 82 million US Galaxy devices from late October, a network that processed over $5.25 trillion in stablecoin volume in 2026.
- Grayscale's Zcash ETF topped $1 billion across its first 30 trading days, placing the privacy coin fund in the top 1% of ETFs launched in the past decade.
- Greece plans a 10% crypto tax from 2027, down from the 15% floated in June, placing it among Europe's low-tax crypto countries beside Cyprus.
- Hunter Biden said LAPTOP's market maker should buy it all back and burn it, after a report found the meme coin pool held under 30,000 tokens at launch.
- Tether signed a memorandum with the National Bank of Kazakhstan to study a tenge-pegged stablecoin and asset tokenization, months after the country amassed a $700 million crypto reserve.
- Coinbase will relaunch its Pro platform by year-end and completed its Deribit integration into Coinbase Global Exchange, uniting US and international crypto options liquidity in one pool.
- The Cardano Foundation spun out Veridian as an independent Swiss company and tokenized most of its 1 million shares, a live case of tokenized equity under CIP-0113.
- Abstract will shut down December 15 after Igloo lost tens of millions funding the Pudgy Penguins-backed Layer 2, with 144 apps and 400,000 users needing to bridge out.
- OpenAI published 722 math manuscripts from an unreleased model, mostly from a single prompt, though only 162 carry a machine-checked Lean proof and mathematicians want receipts.
For the latest updates on digital asset markets, follow us on X @Datawalletcom.
Datawallet Newsletter
Get tomorrow’s issue in your inbox
Join 100,000+ investors · three mornings a week · free forever